Proactive security posture management
Having recognised the limitations of annual pentests, the client realised the need for a dedicated application security team able to design and build product security together with their product team.


Our client, a global leader in secure Virtual Data Rooms for Mergers and Acquisitions (M&A), empowers businesses to safely navigate sensitive information exchange during deals. Their SaaS platform ensures secure cooperation and document sharing between the parties, offering granular access control, advanced analytics, comprehensive project management tools, and additional services to support the deal lifecycle.
During our multi-year cooperation, we improved product security by addressing security at each development phase and adopting robust security mechanisms to mitigate potential risks and prevent security incidents. We established proactive security processes, having streamlined and documented practices for enhanced clarity, stability, and logical flow.
Having recognised the limitations of annual pentests, the client realised the need for a dedicated application security team able to design and build product security together with their product team.
The need for well-documented security processes to ensure consistent application and efficient knowledge transfer. The security processes are to be simple, logical, nicely described and stable so that new engineers could nicely adopt them.
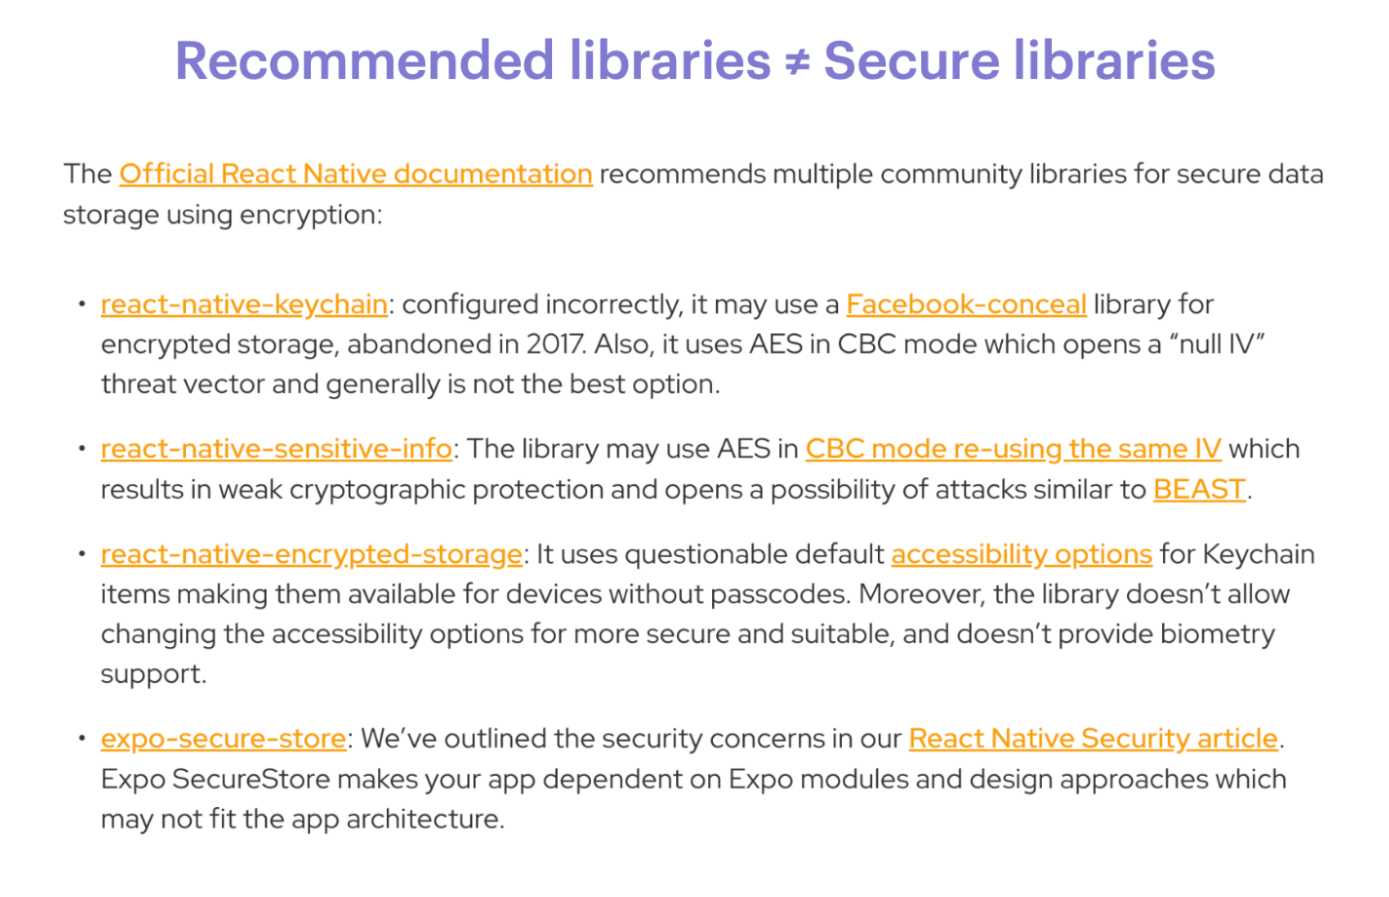
Security should be suitable for the new technological stack. The development team should adapt security strategies to the specifics of React Native, as well as incorporate additional robust security measures, tailored to the nuances of cross-platform framework.
Shifted security efforts from firefighting to proactive work
We managed to make security a seamless part of the workflow, fostering clear communication between product and development teams. We enabled transition from reactive "firefighting" to a proactive security posture, while simplifying security processes and making them well-documented, simple, stable, and logical.
Making security less frustrating for the product team
We led and maintained SSDLC and security processes the [REDACTED] company didn’t have at the very beginning of our cooperation. By regularly providing knowledge base and expert assistance for development and QA teams, we enhanced cooperation within the teams. We tailored security to product goals and clients’ expectations, maintained flexible security architecture and enhanced security posture of our client’s platform.
Stable 80% security score for 2 years
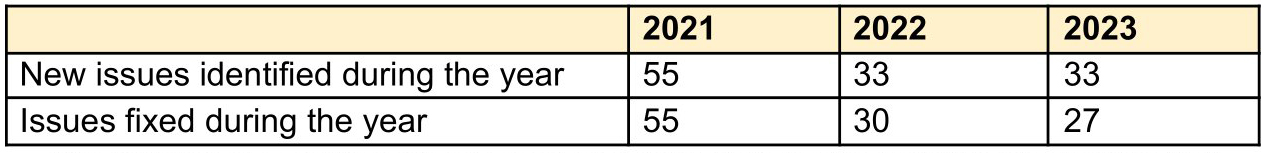
Stable security score and not growing backlog are the achievements of our long and fruitful cooperation with the client. Measurable results and the ability to track them through the years helps in defining the security roadmap of the product and enhance security even further. As a result, no issues were found during recent external penetration testing, making our client satisfied with our cooperation.
Client satisfaction via enhanced security
From now on our client’s platform has all the security controls that their customers typically require. So when our client receive security questionnaires and RFIs, they can provide clear and thorough answers promptly. Thus our client gets satisfied customers and we get a satisfied client.
Contributing to evidence-based reputation on the market
As of today, our client has a well-educated team, timely and effectively managing all security processes. Stable strong security posture, proactive security approach, little-to-no emergency situations, smooth and well-managed security processes make our client and their software platform attractive on the market.
Let’s start a conversation.
Get whitepaper
Apply for the position
Our team will review your resume and provide feedback
within 5 business days