Strong insider risks.
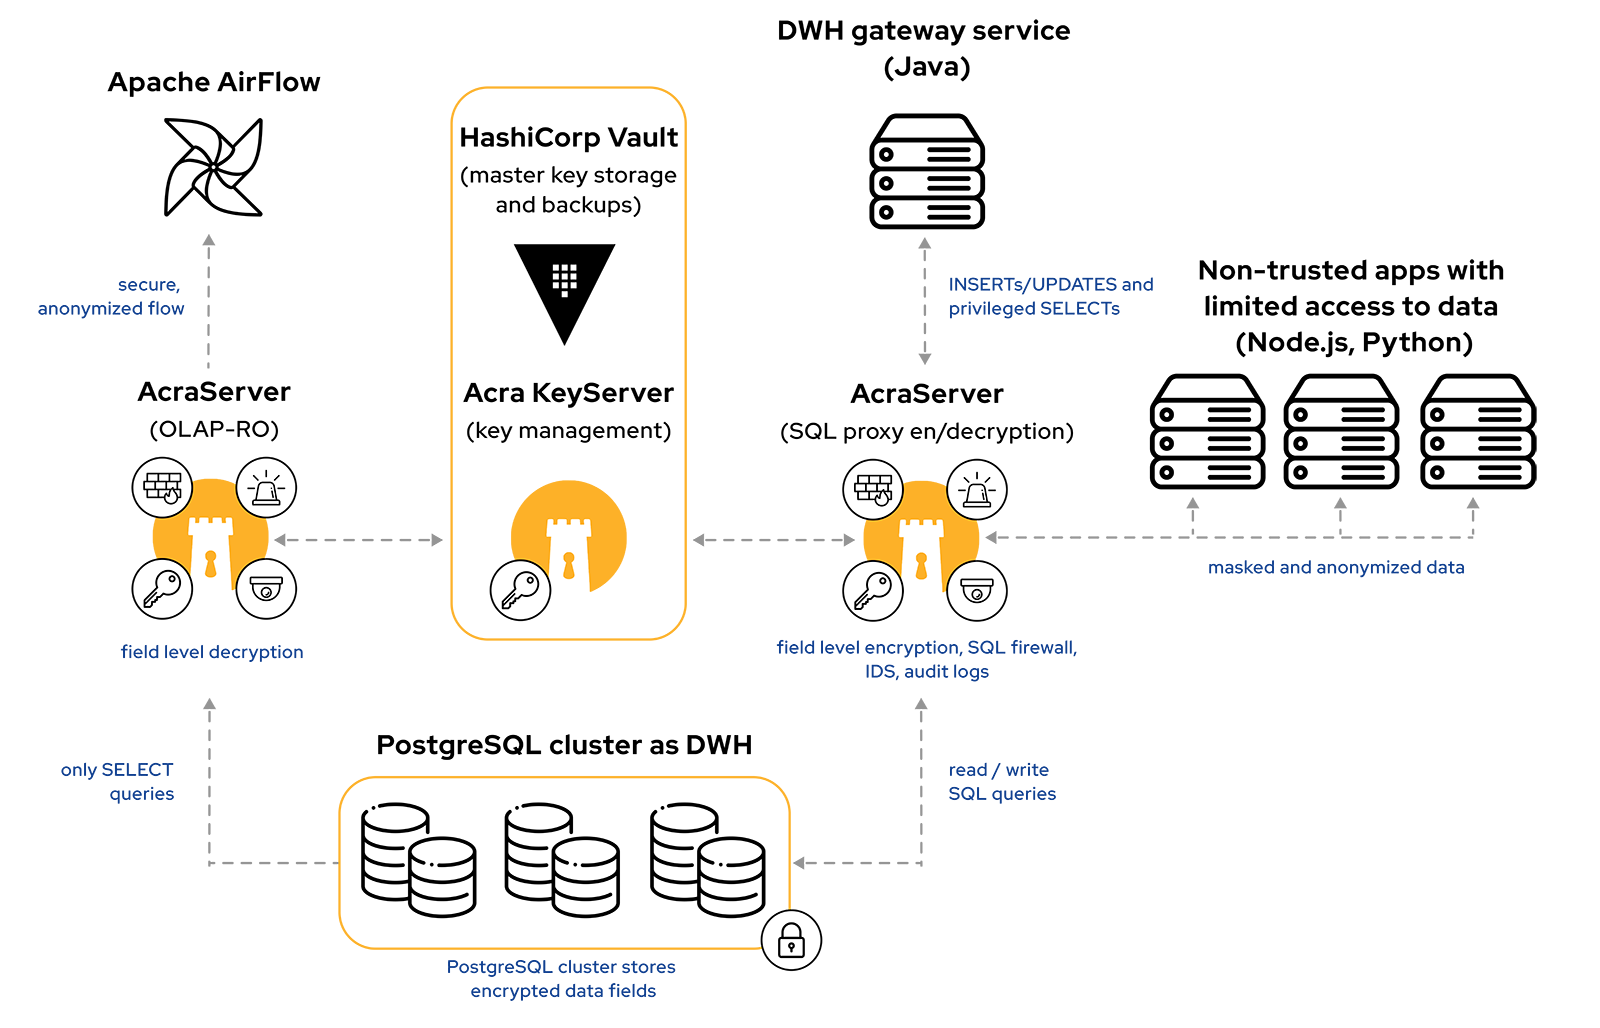
[REDACTED] employs many personnel: developers, DBAs, internal cloud ops. A lot of people need access to the database and applications, yet should not have access to the actual sensitive data. Prior to this project, this requirement was achieved by the security team tightly controlling “who gets what” on a per-request basis, and trusted ops engineers with full access having to agree on each access case with security. The [REDACTED] understood that “manual access control” was exhausting and was looking to a centralized data security solution.