Matomo

IIoT security: protecting specialised edge ML devices | Cossack Labs
Case studies
IIoT security: protecting specialised edge ML devices

IIoT security: protecting specialised edge ML devices

HOT SUMMER 2022 Industrial IoT AI / ML Security architecture SSDLC
IIoT security: protecting specialised edge ML devices

Overview

Industry

  • IIoT security
  • AI / ML security
  • Soil enrichment

Technology stack

  • Python, Django & PostgreSQL
  • GCP cloud + on-prem
  • ML / TensorFlow
  • Raspberry PI 4, Raspberry OS

Regulations / standards

  • GDPR
  • IEC standards
  • NIST RMF, SP 800-53, SP 800-57, SP 800-213, NISTIR 8259 series

Challenges

[01]

Hardened but maintainable IIoT devices

To make reverse engineering more complicated, the operating system should be hardened, all unnecessary packages removed, and default accesses disabled. At the same time, a device should have enough functionality to ensure maintenance and updates.

[02]

Thing you have, thing you know

Devices are “linked” to their operators, allowing only authorised personnel to interact with a device and receive data. The protection should go beyond simple account passwords, and operator and device location can often change.

[03]

Heterogeneous ecosystem

Each ecosystem component has its characteristics and applicable risks: security controls for IIoT devices and fleet management backend are pretty different, and the protection of ML models is generally a separate issue. Adding security into such a system should improve its resilience without adding fragility.

Technology requirements

Technology requirements

Data and IP protection

Telemetry data, ML models, logs, access credentials—if the device operates data, it should protect it during the whole lifecycle.

Fleet management

There should be a way to provision and operate devices at scale. Assemble, upload and automatically harden firmware, upload applications and data, and verify that the system works. Monitor, update remotely, flag as compromised.

Protection against reverse engineering and tampering

Small devices can be lost or stolen. They should be resilient against attempts to reverse engineer, connect, and dig through data.

Our approach

Following NIST standards

As this project lies at the intersection of regulations and industries, we selected NIST standards as a source of requirements, especially SP 800-37, SP 800-53, SP 800-57, and SP 800-213. While following standards word-by-word is overkill, using them as a baseline allowed us to build well-rounded security defences.

Full lifecycle, coordinated security controls

The ecosystem contains multiple parts: operations on devices, communication between devices and centralised server, fleet management, ML models training, etc. Security protection measures follow sensitive assets lifecycle and go through all layers.

Securing a pipeline, not just software

When building thousands of IIoT devices, we pay attention to the security of a particular device and the security of the production and provisioning pipeline. Looking at security from a bird's eye helps to mitigate supply chain risks as early as possible.
Our approach

Solution

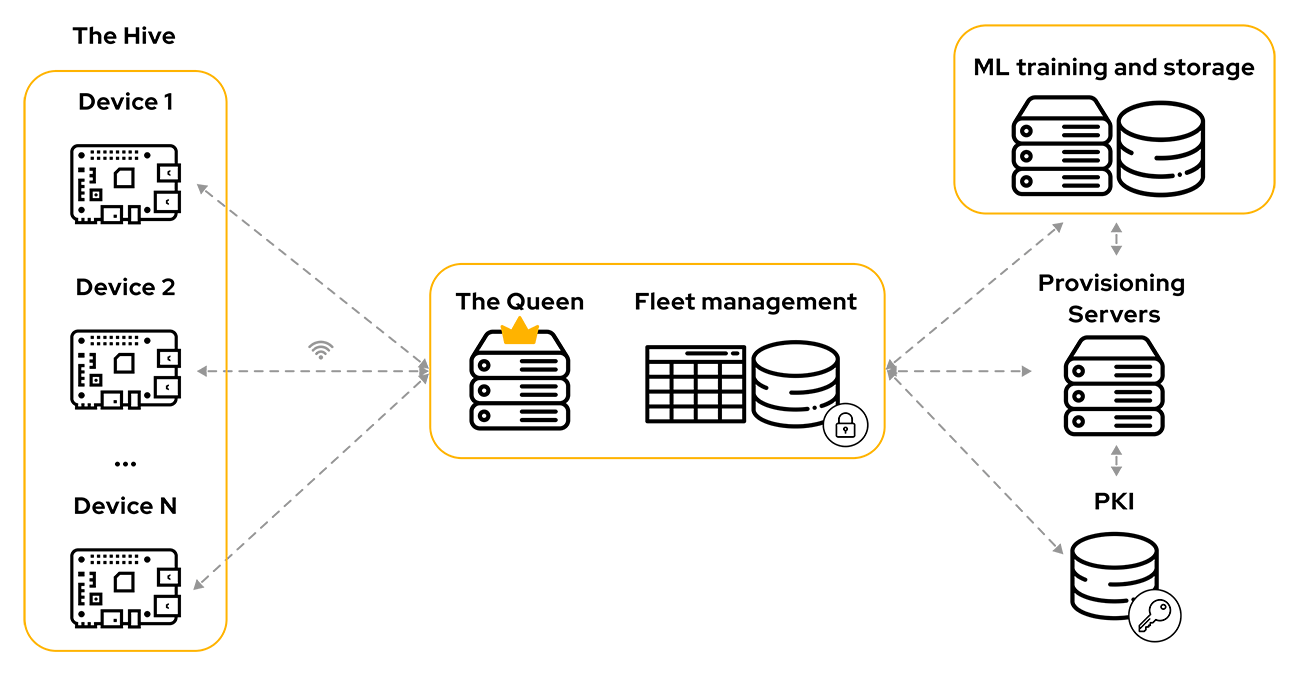
Architecture scheme

Protecting IIoT devices: a Hive of devices communicates with a Queen server, security and cryptography solution by Cossack Labs.

Threat modelling

SSDLC

IIoT device provisioning pipeline

Linux hardening

Fleet management

Application security

Authentication

Machine Learning security

Data at rest security

Encryption and key management

Secure communication

Reverse engineering protections and self-destruction

Protection against side-channel attacks

Results and outcomes

The fields are properly fertilised, and sunflowers are growing in peace, monitored by the Hive and the Queen. This project confirms that information security is more than a technology function but is a business enabler for some industries.

Now, the [REDACTED] company can securely produce and provision IIoT devices, process field data, and update the firmware and ML models. With a mesh of security controls and reverse engineering protections, the [REDACTED] company is confident that competitors won't be able to steal the IP or abuse devices easily.


Up next

Got a challenge that's still standing?

Let’s start a conversation.

Start a conversation

Get whitepaper

Application form

Our team will review your resume and provide feedback
within 5 business days

Thank you!

We’ve received your request and will respond soon.

Your resume has been sent!

Our team will review your resume and provide feedback
within 5 business days